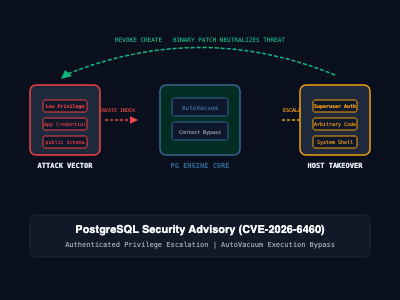
PostgreSQL just dropped an emergency patch for CVE-2026-6460, a high-severity privilege escalation flaw. If you allow untrusted users to create objects, they can hijack the postgres superuser account via manipulated index functions. This guide breaks down the exploit mechanics, fleet audit queries, and zero-downtime patching strategies to lock down your relational clusters. #PostgreSQL #CVE2026 #Cybersecurity #DBA #DevOps #SRE #Infosec #DatabaseSecurity #SQL #Postgres #AppSec

Our Products