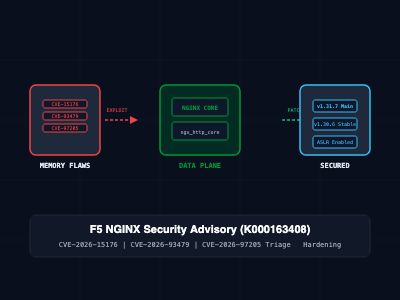
F5 released emergency security updates for NGINX Open Source and NGINX Plus addressing three high-severity memory corruption flaws: CVE-2026-15176 (heap buffer overflow via alias rewrite), CVE-2026-93479 (heap overflow via map regex captures), and CVE-2026-97205 (use-after-free via AIO and SSI). Learn how to audit vulnerable directives, configure immediate mitigations, and patch production ingress controllers. #NGINX #F5 #Cybersecurity #Infosec #DevOps #SRE #AppSec #DevSecOps #Linux #SysAdmin
Our Products