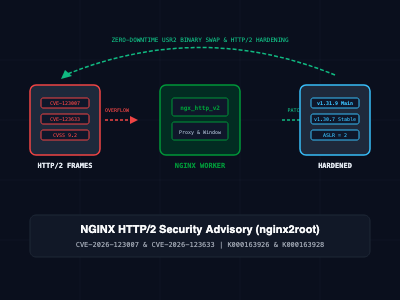
F5 disclosed two critical CVSS 9.2 NGINX HTTP/2 vulnerabilities—CVE-2026-123007 (nginx2root integer underflow heap overflow) and CVE-2026-123633 (proxy use-after-free under low worker_connections). Both enable unauthenticated DoS or RCE on data planes. Learn root causes, audit scripts, temporary HTTP/2 mitigations, and zero-downtime patching to 1.31.9/1.30.7. #NGINX #CVE2026 #nginx2root #HTTP2 #Cybersecurity #DevSecOps #SRE #DevOps #Infosec #Linux #AppSec

Our Products